CCNA 3 v7.0 Final Exam Answers – Enterprise Networking, Security, and Automation
Course Final Exam for Enterprise Networking, Security, and Automation (ENSA v7.0). This comprehensive study guide covers all modules of CCNA 3 v7.0, including OSPF, network security, WAN concepts, QoS, and network automation.
1. Which design feature will limit the size of a failure domain in an enterprise network?
Explanation: In order to best limit the of a failure domain, routers or multilayer switches can be deployed in pairs. The failure of a single device should not cause the network to go down. Installing redundant power supplies may protect a single device from a power failure, but if that device suffers from another type of problem, a redundant device would have been a better solution. Purchasing enterprise equipment that handles large flows of traffic will not provide extra reliability in times of an outage. If a collapsed core design is used, the core and distribution are collapsed into a single device, increasing the chance of a devastating outage.
2. Which two things should a network administrator modify on a router to perform password recovery? (Choose two.)
Explanation: Password recovery requires modifying the configuration register to bypass the startup configuration and then resetting the password.
3. What type of network uses one common infrastructure to carry voice, data, and video signals?
Explanation: A converged network has only one physical network to install and manage. This results in substantial savings over the installation and management of separate voice, video, and data networks.
4. What are three advantages of using private IP addresses and NAT? (Choose three.)
Explanation: Private IP addresses are designed to be exclusively used for internal networks and they cannot be used on the Internet. Thus they are not visible directly from the Internet and they can be used freely by network administrators for internal networks. In order for the internal hosts to access the Internet, NAT is used to translate between private and public IP addresses. NAT takes an internal private IP address and translates it to a global public IP address before the packet is forwarded.
5. Which two scenarios are examples of remote access VPNs? (Choose two.)
Explanation: Remote access VPNs connect individual users to another network via a VPN client that is installed on the user device. Site-to-site VPNs are “always on” connections that use VPN gateways to connect two sites together. Users at each site can access the network on the other site without having to use any special clients or configurations on their individual devices.
6. What are three benefits of cloud computing? (Choose three.)
Explanation: Cloud computing provides on-demand services, reduces onsite equipment needs, and enables access from anywhere.
7. What is a characteristic of a single-area OSPF network?
Explanation: In a single-area OSPF network, all routers are in the backbone area (area 0).
8. What is a WAN?
Explanation: A WAN (Wide Area Network) spans a large geographic area and connects multiple LANs.
9. A network administrator has been tasked with creating a disaster recovery plan. As part of this plan, the administrator is looking for a backup site for all of the data on the company servers. What service or technology would support this requirement?
Explanation: A data center provides the infrastructure for backup and disaster recovery.
10. Which type of OSPF packet is used by a router to discover neighbor routers and establish neighbor adjacency?
Explanation: Hello packets are used to discover and maintain neighbor relationships in OSPF.
11. Which two statements are characteristics of a virus? (Choose two.)
Explanation: The type of end user interaction required to launch a virus is typically opening an application, opening a web page, or powering on the computer. Once activated, a virus may infect other files located on the computer or other computers on the same network.
12. Which public WAN access technology utilizes copper telephone lines to provide access to subscribers that are multiplexed into a single T3 link connection?
Explanation: DSL uses copper telephone lines and can be multiplexed into T3 connections.
13. A customer needs a metropolitan area WAN connection that provides high-speed, dedicated bandwidth between two sites. Which type of WAN connection would best fulfill this need?
Explanation: MPLS can use a variety of underlying technologies such as T- and E-Carriers, Carrier Ethernet, ATM, Frame Relay, and DSL, all of which support lower speeds than an Ethernet WAN. Neither a circuit-switched network, such as the public switched telephone network (PSTN) or Integrated Service Digital Network (ISDN), nor a packet-switched network, is considered high speed.
14. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use debuggers?
Explanation: Debuggers are used to reverse engineer binaries and analyze malware during penetration testing.
15. Consider the following output for an ACL that has been applied to a router via the access-class in command. What can a network administrator determine from the output that is shown?
R1#
Standard IP access list 2
10 permit 192.168.10.0, wildcard bits 0.0.0.255 (2 matches)
20 deny any (1 match)
Explanation: The access-class command is used only on VTY ports. VTY ports support Telnet and/or SSH traffic. The match permit ACE is how many attempts were allowed using the VTY ports. The match deny ACE shows that a device from a network other than 192.168.10.0 was not allowed to access the router through the VTY ports.
16. What command would be used as part of configuring NAT or PAT to clear dynamic entries before the timeout has expired?
Explanation: The clear ip nat translation command clears dynamic NAT entries.
17. What are two characteristics of video traffic? (Choose two.)
Explanation: Video traffic is bursty and requires low latency; acceptable latency is up to 400 ms.
18. Refer to the exhibit. A technician is configuring R2 for static NAT to allow the client to access the web server. What is a possible reason that the client PC cannot access the web server?
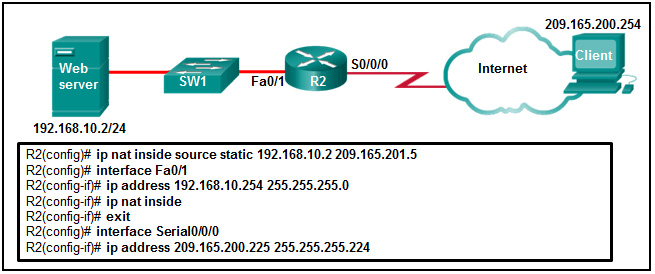
Explanation: Interface S0/0/0 should be identified as the outside NAT interface. The command to do this would be R2(config-if)# ip nat outside.
19. In setting up a small office network, the network administrator decides to assign private IP addresses dynamically to workstations and mobile devices. Which feature must be enabled on the company router in order for office devices to access the internet?
Explanation: Network Address Translation (NAT) is the process used to convert private addresses to internet-routable addresses that allow office devices to access the internet.
20. A data center has recently updated a physical server to host multiple operating systems on a single CPU. The data center can now provide each customer with a separate web server without having to allocate an actual discrete server for each customer. What is the networking trend that is being implemented by the data center in this situation?
Explanation: Virtualization allows multiple operating systems to run on a single physical server.
21. Refer to the exhibit. Which address or addresses represent the inside global address?
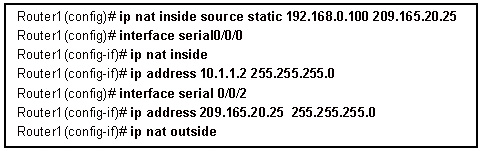
Explanation: The inside global address is the public address used for NAT translation (209.165.20.25).
22. Which two IPsec protocols are used to provide data integrity?
Explanation: The IPsec framework uses various protocols and algorithms to provide data confidentiality, data integrity, authentication, and secure key exchange. Two popular algorithms used to ensure that data is not intercepted and modified (data integrity) are MD5 and SHA. AES is an encryption protocol and provides data confidentiality. DH (Diffie-Hellman) is an algorithm used for key exchange. RSA is an algorithm used for authentication.
23. If an outside host does not have the Cisco AnyConnect client preinstalled, how would the host gain access to the client image?
Explanation: If an outside host does not have the Cisco AnyConnect client preinstalled, the remote user must initiate a clientless SSL VPN connection via a compliant web browser, and then download and install the AnyConnect client on the remote host.
24. A company is considering updating the campus WAN connection. Which two WAN options are examples of the private WAN architecture? (Choose two.)
Explanation: Leased lines and Ethernet WAN are examples of private WAN infrastructure.
25. Which type of QoS marking is applied to Ethernet frames?
Explanation: The class of service (CoS) marking allows a Layer 2 Ethernet frame to be marked with eight levels of priority (values 0–7). This marking can be used by QoS-enabled network devices to provide preferential traffic treatment.
26. Refer to the exhibit. Routers R1 and R2 are connected via a serial link. One router is configured as the NTP master, and the other is an NTP client. Which two pieces of information can be obtained from the partial output of the show ntp associations detail command on R2? (Choose two.)
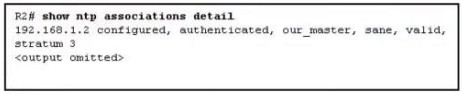
Explanation: The NTP association output shows the master (R1) and client (R2) relationship.
27. Refer to the exhibit. The network administrator that has the IP address of 10.0.70.23/25 needs to have access to the corporate FTP server (10.0.54.5/28). The FTP server is also a web server that is accessible to all internal employees on networks within the 10.x.x.x address. No other traffic should be allowed to this server. Which extended ACL would be used to filter this traffic, and how would this ACL be applied? (Choose two.)
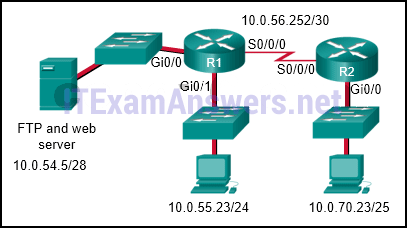
Explanation: The first two lines of the ACL allow host 10.0.70.23 FTP access to the server that has the IP address of 10.0.54.5. The next line of the ACL allows HTTP access to the server from any host that has an IP address that starts with the number 10. The fourth line of the ACL denies any other type of traffic to the server from any source IP address. The last line of the ACL permits anything else in case there are other servers or devices added to the 10.0.54.0/28 network. Because traffic is being filtered from all other locations and for the 10.0.70.23 host device, the best place to put this ACL is closest to the server.
28. Refer to the exhibit. If the network administrator created a standard ACL that allows only devices that connect to the R2 G0/0 network access to the devices on the R1 G0/1 interface, how should the ACL be applied?
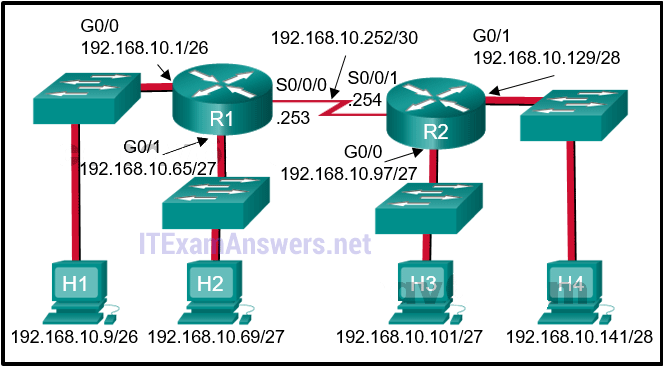
Explanation: Because standard access lists only filter on the source IP address, they are commonly placed closest to the destination network. In this example, the source packets will be coming from the R2 G0/0 network. The destination is the R1 G0/1 network. The proper ACL placement is outbound on the R1 G0/1 interface.
29. Which is a characteristic of a Type 2 hypervisor?
Explanation: Type 2 hypervisors are hosted on an underlaying operating system and are best suited for consumer applications and those experimenting with virtualization. Unlike Type 1 hypervisors, Type 2 hypervisors do not require a management console and do not have direct access to hardware.
30. What are the two types of VPN connections? (Choose two.)
Explanation: The two main types of VPNs are site-to-site and remote access.
31. Refer to the exhibit. What three conclusions can be drawn from the displayed output? (Choose three.)
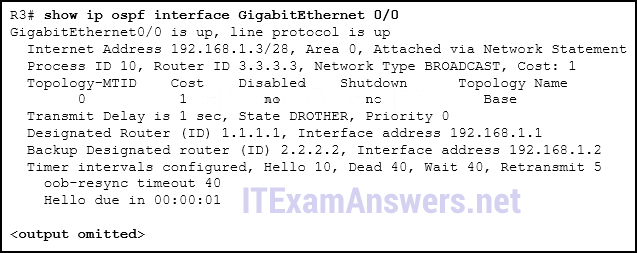
Explanation: The OSPF output shows DR/BDR election details and hello timer information.
32. Refer to the exhibit. A network administrator is configuring an ACL to limit the connection to R1 vty lines to only the IT group workstations in the network 192.168.22.0/28. The administrator verifies the successful Telnet connections from a workstation with IP 192.168.22.5 to R1 before the ACL is applied. However, after the ACL is applied to the interface Fa0/0, Telnet connections are denied. What is the cause of the connection failure?
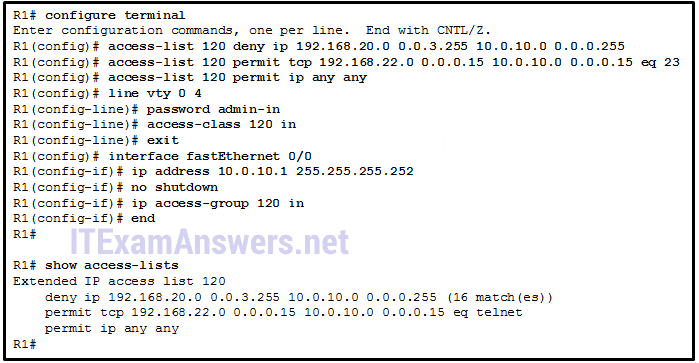
Explanation: The source IP range in the deny ACE is 192.168.20.0 0.0.3.255, which covers IP addresses from 192.168.20.0 to 192.168.23.255. The IT group network 192.168.22.0/28 is included in the 192.168.20/22 network. Therefore, the connection is denied. To fix it, the order of the deny and permit ACE should be switched.
33. What functionality does mGRE provide to the DMVPN technology?
Explanation: DMVPN is built on three protocols, NHRP, IPsec, and mGRE. NHRP is the distributed address mapping protocol for VPN tunnels. IPsec encrypts communications on VPN tunnels. The mGRE protocol allows the dynamic creation of multiple spoke tunnels from one permanent VPN hub.
34. What is used to pre-populate the adjacency table on Cisco devices that use CEF to process packets?
Explanation: CEF uses the ARP table to pre-populate the adjacency table for fast forwarding.
35. What command would be used as part of configuring NAT or PAT to display information about NAT configuration parameters and the number of addresses in the pool?
Explanation: show ip nat statistics displays NAT configuration and pool information.
36. What is a purpose of establishing a network baseline?
Explanation: A baseline is used to establish normal network or system performance. It can be used to compare with future network or system performances in order to detect abnormal situations.
37. Match the type of WAN device or service to the description. (Not all options are used.)
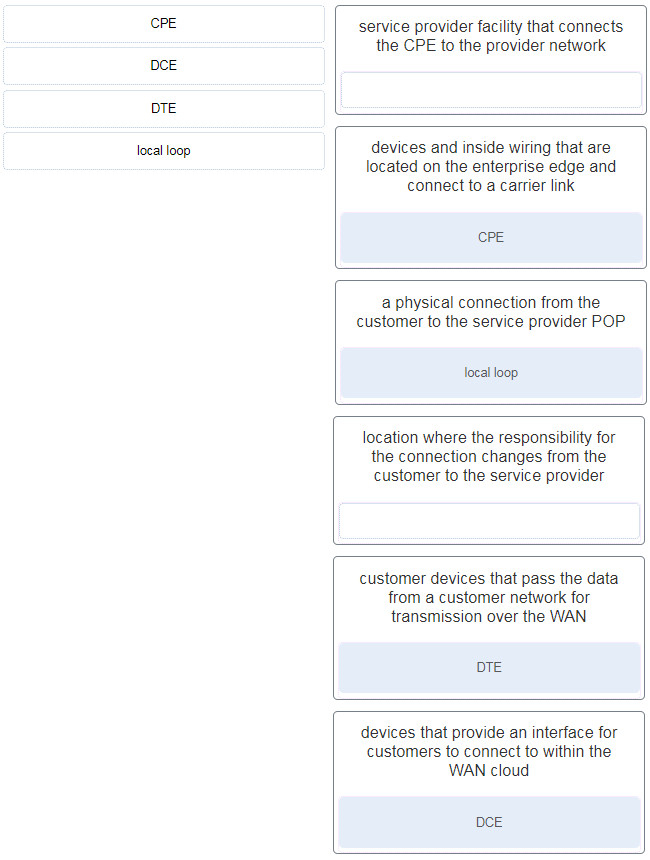
Explanation: Topic 7.1 – Match each WAN component to its description.
| Device/Service | Description |
|---|---|
| CPE | devices and inside wiring that are located on the enterprise edge and connect to a carrier link |
| DCE | devices that provide an interface for customers to connect to within the WAN cloud |
| DTE | customer devices that pass the data from a customer network for transmission over the WAN |
| local loop | a physical connection from the customer to the service provider POP |
38. Which statement describes a characteristic of standard IPv4 ACLs?
Explanation: A baseline is used to establish normal network or system performance. It can be used to compare with future network or system performances in order to detect abnormal situations.
39. Refer to the exhibit. R1 is configured for NAT as displayed. What is wrong with the configuration?
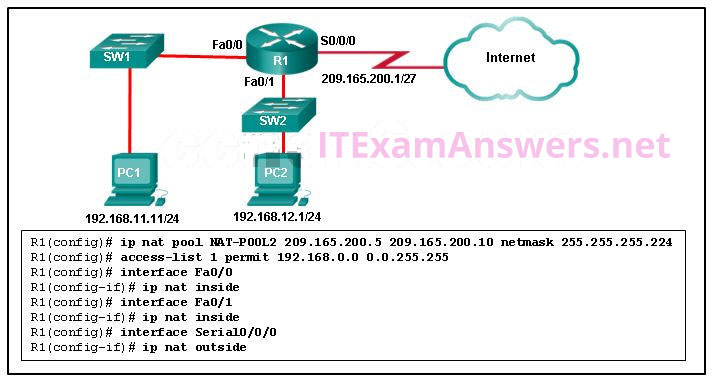
Explanation: R1 has to have NAT-POOL2 bound to ACL 1. This is accomplished with the command R1(config)#ip nat inside source list 1 pool NAT-POOL2. This would enable the router to check for all interesting traffic and if it matches ACL 1 it would be translated by use of the addresses in NAT-POOL2.
40. Refer to the exhibit. What method can be used to enable an OSPF router to advertise a default route to neighboring OSPF routers?
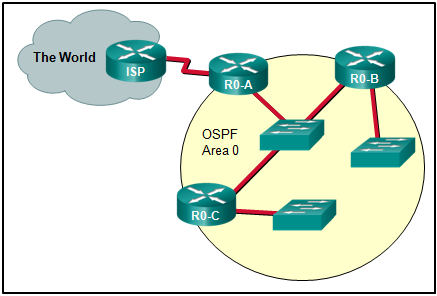
Explanation: The default-information originate command advertises a default route in OSPF.
41. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use applications such as John the Ripper, THC Hydra, RainbowCrack, and Medusa?
Explanation: These tools are used for password cracking in penetration testing.
42. What are two syntax rules for writing a JSON array? (Choose two.)
Explanation: A JSON array is a collection of ordered values within square brackets [ ]. The values in the array are separated by a comma. For example “users” : [“bob”, “alice”, “eve”].
43. What is a characteristic of a Trojan horse as it relates to network security?
Explanation: A Trojan horse carries out malicious operations under the guise of a legitimate program. Denial of service attacks send extreme quantities of data to a particular host or network device interface. Password attacks use electronic dictionaries in an attempt to learn passwords. Buffer overflow attacks exploit memory buffers by sending too much information to a host to render the system inoperable.
44. An attacker is redirecting traffic to a false default gateway in an attempt to intercept the data traffic of a switched network. What type of attack could achieve this?
Explanation: In DHCP spoofing attacks, an attacker configures a fake DHCP server on the network to issue DHCP addresses to clients with the aim of forcing the clients to use a false default gateway, and other false services. DHCP snooping is a Cisco switch feature that can mitigate DHCP attacks. MAC address starvation and MAC address snooping are not recognized security attacks. MAC address spoofing is a network security threat.
45. A company is developing a security policy for secure communication. In the exchange of critical messages between a headquarters office and a branch office, a hash value should only be recalculated with a predetermined code, thus ensuring the validity of data source. Which aspect of secure communications is addressed?
Explanation: Secure communications consists of four elements: Data confidentiality – guarantees that only authorized users can read the message Data integrity – guarantees that the message was not altered Origin authentication – guarantees that the message is not a forgery and does actually come from whom it states Data nonrepudiation – guarantees that the sender cannot repudiate, or refute, the validity of a message sent
46. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use packet sniffers?
Explanation: Packet sniffers capture and analyze network traffic.
47. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 172.20.0.0 255.255.252.0. What wildcard mask would the administrator use in the OSPF network statement?
Explanation: The wildcard mask for 255.255.252.0 is 0.0.3.255.
48. Match the HTTP method with the RESTful operation.
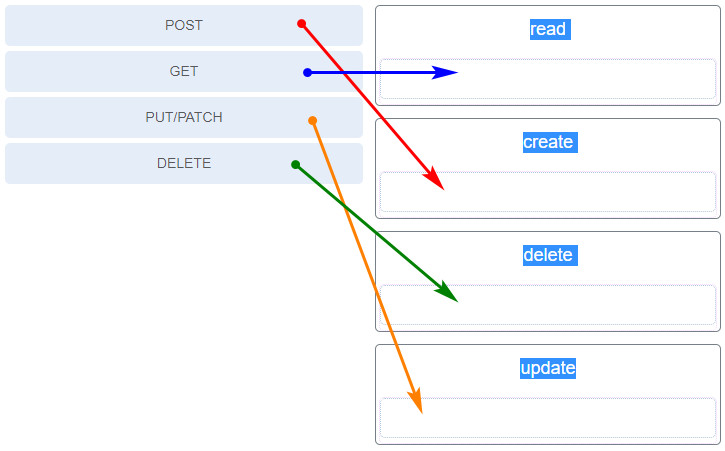
Explanation: RESTful operations map to HTTP methods.
| HTTP Method | RESTful Operation |
|---|---|
| POST | Create |
| GET | Read |
| PUT/PATCH | Update/Replace/Modify |
| DELETE | Delete |
49. Refer to the exhibit. What is the OSPF cost to reach the West LAN 172.16.2.0/24 from East?
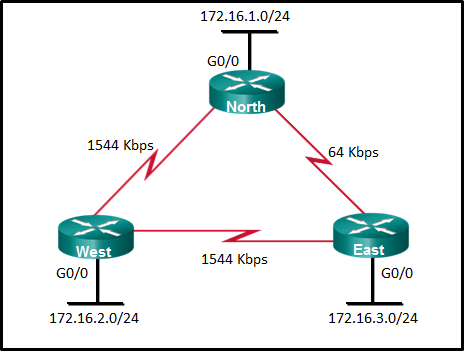
Explanation: The OSPF cost is calculated based on interface bandwidth; the total cost is 65.
50. What is one reason to use the ip ospf priority command when the OSPF routing protocol is in use?
Explanation: The OSPF priority can be set to a number between 0 and 255. The higher the number set, the more likely the router becomes the DR. A priority 0 stops a router from participating in the election process and the router does not become a DR or a BDR.
51. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
access-list 210 permit tcp 172.18.20.0 0.0.0.31 172.18.20.32 0.0.0.31 eq ftp .
If a packet with a source address of 172.18.20.14, a destination address of 172.18.20.40, and a protocol of 21 is received on the interface, is the packet permitted or denied?
Explanation: The source (172.18.20.14) and destination (172.18.20.40) match the ACL, and port 21 is FTP, so it is permitted.
52. What is a characteristic of the two-tier spine-leaf topology of the Cisco ACI fabric architecture?
Explanation: In spine-leaf topology, leaf switches connect to spines but not to each other.
53. Which two scenarios would result in a duplex mismatch? (Choose two.)
Explanation: Duplex mismatch occurs when one side is set to full-duplex and the other to half-duplex, or when autonegotiation fails.
54. A network technician is configuring SNMPv3 and has set a security level of auth. What is the effect of this setting?
Explanation: SNMPv3 auth level uses HMAC-MD5 or HMAC-SHA for authentication.
55. What are two types of attacks used on DNS open resolvers? (Choose two.)
Explanation: Three types of attacks used on DNS open resolvers are as follows:DNS cache poisoning – attacker sends spoofed falsified information to redirect users from legitimate sites to malicious sites DNS amplification and reflection attacks – attacker sends an increased volume of attacks to mask the true source of the attack DNS resource utilization attacks – a denial of service (DoS) attack that consumes server resources
56. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
access-list 101 permit udp 192.168.100.0 0.0.2.255 64.100.40.0 0.0.0.15 eq telnet .
If a packet with a source address of 192.168.101.45, a destination address of 64.100.40.4, and a protocol of 23 is received on the interface, is the packet permitted or denied?
Explanation: The ACL specifies UDP, but Telnet uses TCP (port 23), so the packet is denied.
57. Which type of resources are required for a Type 1 hypervisor?
Explanation: Type 1 hypervisors require a management console for administration.
58. In JSON, what is held within square brackets [ ]?
Explanation: Square brackets in JSON denote an array.
59. What are three components used in the query portion of a typical RESTful API request? (Choose three.)
Explanation: RESTful API queries include format, key, and parameters.
60. A user reports that when the corporate web page URL is entered on a web browser, an error message indicates that the page cannot be displayed. The help-desk technician asks the user to enter the IP address of the web server to see if the page can be displayed. Which troubleshooting method is being used by the technician?
Explanation: The technician is using divide-and-conquer by testing IP connectivity to isolate the issue.
61. Which protocol provides authentication, integrity, and confidentiality services and is a type of VPN?
Explanation: IPsec services allow for authentication, integrity, access control, and confidentiality. With IPsec, the information exchanged between remote sites can be encrypted and verified. Both remote-access and site-to-site VPNs can be deployed using IPsec.
62. Which statement describes a characteristic of Cisco Catalyst 2960 switches?
Explanation: Cisco Catalyst 2960 switches support one active switched virtual interface (SVI) with IOS versions prior to 15.x. They are commonly used as access layer switches and they are fixed configuration switches.
63. Which component of the ACI architecture translates application policies into network programming?
Explanation: The APIC translates application policies into network programming in ACI.
64. Which two pieces of information should be included in a logical topology diagram of a network? (Choose two.)
Explanation: The interface identifier and connection type should be included in a logical topology diagram because they indicate which interface is connected to other devices in the network with a specific type such as LAN, WAN, point-to-point, etc. The OS/IOS version, device type, cable type and identifier, and cable specification are typically included in a physical topology diagram.
65. Refer to the exhibit. A PC at address 10.1.1.45 is unable to access the Internet. What is the most likely cause of the problem?
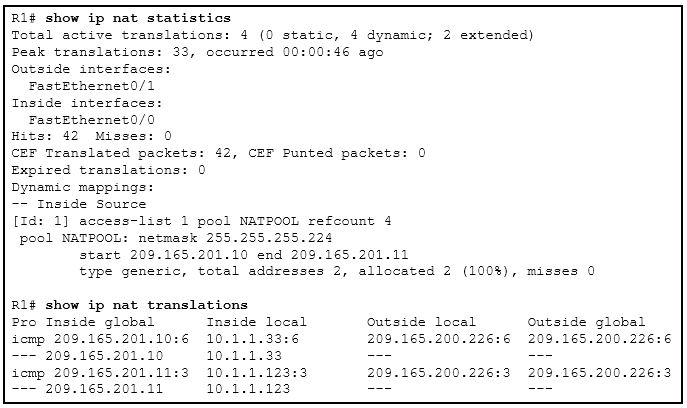
Explanation: The output of show ip nat statistics shows that there are 2 total addresses and that 2 addresses have been allocated (100%). This indicates that the NAT pool is out of global addresses to give new clients. Based on the show ip nat translations, PCs at 10.1.1.33 and 10.1.1.123 have used the two available addresses to send ICMP messages to a host on the outside network.
66. What are two benefits of using SNMP traps? (Choose two.)
Explanation: SNMP traps reduce polling and network load by sending notifications only when events occur.
67. Which statement accurately describes a characteristic of IPsec?
Explanation: IPsec is an open standards framework that provides security at the network layer.
68. In a large enterprise network, which two functions are performed by routers at the distribution layer? (Choose two.)
Explanation: In a large enterprise network, the provision of a high-speed network backbone is a function of the core layer. Access layer switches connect users to the network and provide Power over Ethernet to devices. Distribution layer routers provide data traffic security and connections to other networks.
69. Which two statements describe the use of asymmetric algorithms? (Choose two.)
Explanation: Asymmetric algorithms use two keys: a public key and a private key. Both keys are capable of the encryption process, but the complementary matched key is required for decryption. If a public key encrypts the data, the matching private key decrypts the data. The opposite is also true. If a private key encrypts the data, the corresponding public key decrypts the data.
70. Refer to the exhibit. A network administrator has deployed QoS and has configured the network to mark traffic on the VoIP phones as well as the Layer 2 and Layer 3 switches. Where should initial marking occur to establish the trust boundary?
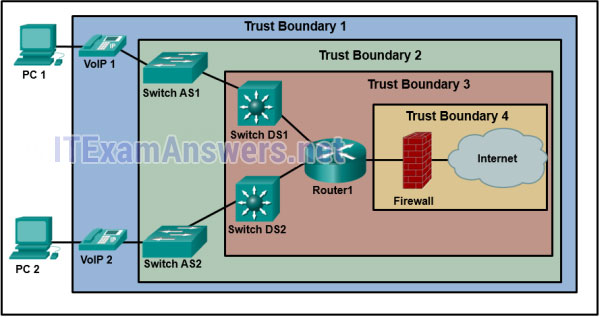
Explanation: Traffic should be classified and marked as close to its source as possible. The trust boundary identifies at which device marked traffic should be trusted. Traffic marked on VoIP phones would be considered trusted as it moves into the enterprise network.
71. What are two benefits of extending access layer connectivity to users through a wireless medium? (Choose two.)
Explanation: Wireless connectivity at the access layer provides increased flexibility, reduced costs, and the ability to grow and adapt to changing business requirements. Utilizing wireless routers and access points can provide an increase in the number of central points of failure. Wireless routers and access points will not provide an increase in bandwidth availability.
72. What are two purposes of launching a reconnaissance attack on a network? (Choose two.)
Explanation: Gathering information about a network and scanning for access is a reconnaissance attack. Preventing other users from accessing a system is a denial of service attack. Attempting to retrieve and modify data, and attempting to escalate access privileges are types of access attacks.
73. A group of users on the same network are all complaining about their computers running slowly. After investigating, the technician determines that these computers are part of a zombie network. Which type of malware is used to control these computers?
Explanation: A botnet is a network of infected computers controlled by an attacker.
74. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
access-list 101 permit tcp 10.1.1.0 0.0.0.255 host 192.31.7.45 eq dns .
If a packet with a source address of 10.1.1.201, a destination address of 192.31.7.45, and a protocol of 23 is received on the interface, is the packet permitted or denied?
Explanation: The ACL permits TCP on port 53 (DNS), but the packet uses protocol 23 (Telnet), so it is denied.
75. Refer to the exhibit. From which location did this router load the IOS?
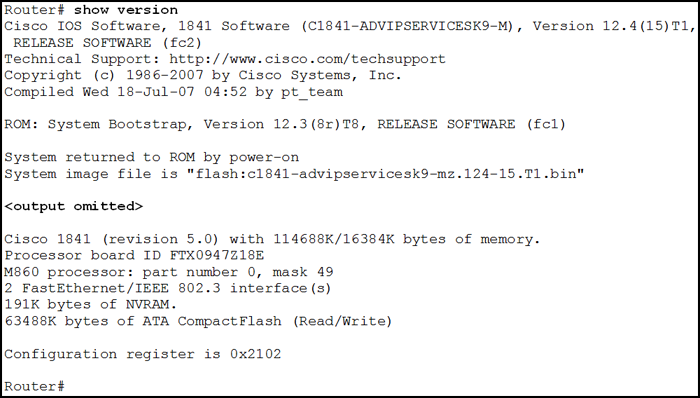
Explanation: The router loaded the IOS from flash memory.
76. Refer to the exhibit. Which data format is used to represent the data for network automation applications?
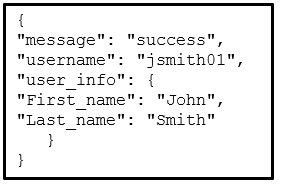
Explanation: The format shown is JSON (JavaScript Object Notation).
77. What QoS step must occur before packets can be marked?
Explanation: Classification must occur before marking to identify which packets to mark.
78. What is the main function of a hypervisor?
Explanation: A hypervisor is a key component of virtualization. A hypervisor is often software-based and is used to create and manage multiple VM instances.
79. A company needs to interconnect several branch offices across a metropolitan area. The network engineer is seeking a solution that provides high-speed converged traffic, including voice, video, and data on the same network infrastructure. The company also wants easy integration to their existing LAN infrastructure in their office locations. Which technology should be recommended?
Explanation: Ethernet WAN uses many Ethernet standards and it connects easily to existing Ethernet LANs. It provides a switched, high-bandwidth Layer 2 network capable of managing data, voice, and video all on the same infrastructure. ISDN, while capable of supporting both voice and data, does not provide high bandwidth. VSAT uses satellite connectivity to establish a private WAN connection but with relatively low bandwidth. Use of VSAT, ISDN, and Frame Relay require specific network devices for the WAN connection and data conversion between LAN and WAN.
80. Refer to the exhibit. As traffic is forwarded out an egress interface with QoS treatment, which congestion avoidance technique is used?
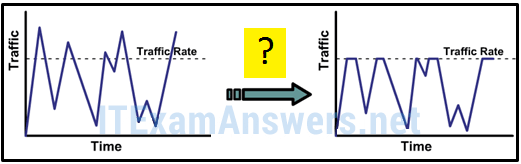
Explanation: Traffic shaping buffers excess packets in a queue and then forwards the traffic over increments of time, which creates a smoothed packet output rate. Traffic policing drops traffic when the amount of traffic reaches a configured maximum rate, which creates an output rate that appears as a saw-tooth with crests and troughs.
81. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
access-list 101 permit tcp 10.1.1.0 0.0.0.255 host 10.1.3.8 eq dns .
If a packet with a source address of 10.1.3.8, a destination address of 10.10.3.8, and a protocol of 53 is received on the interface, is the packet permitted or denied?
Explanation: The source address is 10.1.3.8, but the ACL permits traffic from 10.1.1.0/24, so it is denied.
82. Refer to the exhibit. What is the purpose of the command marked with an arrow shown in the partial configuration output of a Cisco broadband router?
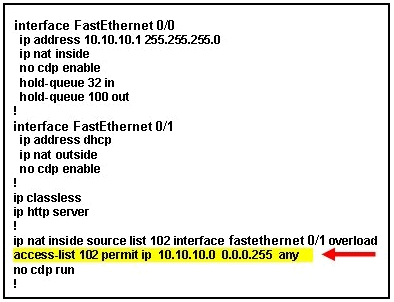
Explanation: The ACL defines the addresses that are subject to NAT translation.
83. If a router has two interfaces and is routing both IPv4 and IPv6 traffic, how many ACLs could be created and applied to it?
Explanation: In calculating how many ACLs can be configured, use the rule of “three Ps”: one ACL per protocol, per direction, per interface. In this case, 2 interfaces x 2 protocols x 2 directions yields 8 possible ACLs.
84. Refer to the exhibit. An administrator first configured an extended ACL as shown by the output of the show access-lists command. The administrator then edited this access-list by issuing the commands below. Which two conclusions can be drawn from this new configuration? (Choose two.)
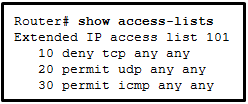
Router(config)# ip access-list extended 101
Router(config-ext-nacl)# no 20
Router(config-ext-nacl)# 5 permit tcp any any eq 22
Router(config-ext-nacl)# 20 deny udp any any
Explanation: After editing, the ACL permits SSH (port 22) and ICMP (ping), but denies other TCP and UDP.
85. Which troubleshooting approach is more appropriate for a seasoned network administrator rather than a less-experienced network administrator?
Explanation: Experienced administrators may use a less-structured approach based on experience and educated guesses.
86. Refer to the exhibit. Many employees are wasting company time accessing social media on their work computers. The company wants to stop this access. What is the best ACL type and placement to use in this situation?
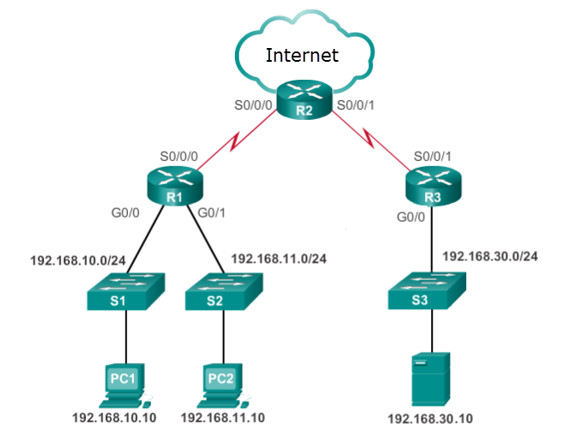
Explanation: Extended ACLs placed close to the source (inbound on R1 interfaces) can block specific traffic types.
87. Refer to the exhibit. An administrator is trying to configure PAT on R1, but PC-A is unable to access the Internet. The administrator tries to ping a server on the Internet from PC-A and collects the debugs that are shown in the exhibit. Based on this output, what is most likely the cause of the problem?
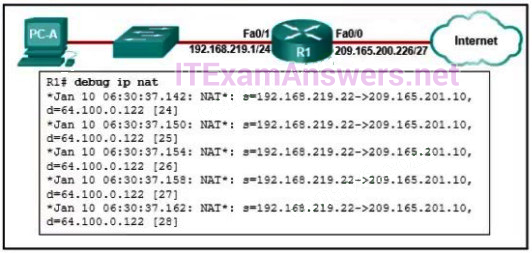
Explanation: The output of debug ip nat shows each packet that is translated by the router. The “s” is the source IP address of the packet and the “d” is the destination. The address after the arrow (“->”) shows the translated address. In this case, the translated address is on the 209.165.201.0 subnet but the ISP facing interface is in the 209.165.200.224/27 subnet. The ISP may drop the incoming packets, or might be unable to route the return packets back to the host because the address is in an unknown subnet.
88. Why is QoS an important issue in a converged network that combines voice, video, and data communications?
Explanation: The output of debug ip nat shows each packet that is translated by the router. The “s” is the source IP address of the packet and the “d” is the destination. The address after the arrow (“->”) shows the translated address. In this case, the translated address is on the 209.165.201.0 subnet but the ISP facing interface is in the 209.165.200.224/27 subnet. The ISP may drop the incoming packets, or might be unable to route the return packets back to the host because the address is in an unknown subnet.
89. Which statement describes a VPN?
Explanation: A VPN is a private network that is created over a public network. Instead of using dedicated physical connections, a VPN uses virtual connections routed through a public network between two network devices.
90. In which OSPF state is the DR/BDR election conducted?
Explanation: DR/BDR election occurs in the Two-Way state.
91. Two corporations have just completed a merger. The network engineer has been asked to connect the two corporate networks without the expense of leased lines. Which solution would be the most cost effective method of providing a proper and secure connection between the two corporate networks?
Explanation: The site-to-site VPN is an extension of a classic WAN network that provides a static interconnection of entire networks. Frame Relay would be a better choice than leased lines, but would be more expensive than implementing site-to-site VPNs. The other options refer to remote access VPNs which are better suited for connecting users to the corporate network versus interconnecting two or more networks.
92. What is the final operational state that will form between an OSPF DR and a DROTHER once the routers reach convergence?
Explanation: OSPF neighbors reach the Full state when they are fully adjacent.
93. Refer to the exhibit. If the switch reboots and all routers have to re-establish OSPF adjacencies, which routers will become the new DR and BDR?
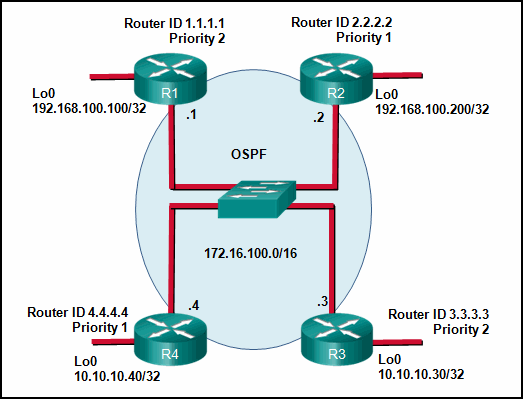
Explanation: R3 has the highest priority and highest router ID, so it becomes DR; R1 becomes BDR.
94. Which type of server would be used to keep a historical record of messages from monitored network devices?
Explanation: A syslog server stores log messages from network devices.
95. When QoS is implemented in a converged network, which two factors can be controlled to improve network performance for real-time traffic? (Choose two.)
Explanation: Delay is the latency between a sending and receiving device. Jitter is the variation in the delay of the received packets. Both delay and jitter need to be controlled in order to support real-time voice and video traffic.
96. In which step of gathering symptoms does the network engineer determine if the problem is at the core, distribution, or access layer of the network?
Explanation: In the “narrow the scope” step of gathering symptoms, a network engineer will determine if the network problem is at the core, distribution, or access layer of the network. Once this step is complete and the layer is identified, the network engineer can determine which pieces of equipment are the most likely cause.
97. What protocol sends periodic advertisements between connected Cisco devices in order to learn device name, IOS version, and the number and type of interfaces?
Explanation: CDP (Cisco Discovery Protocol) advertises device information to neighbors.
98. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 192.168.0.0 255.255.252.0. What wildcard mask would the administrator use in the OSPF network statement?
Explanation: The wildcard mask for 255.255.252.0 is 0.0.3.255.
99. Refer to the exhibit. An administrator configures the following ACL in order to prevent devices on the 192.168.1.0 subnet from accessing the server at 10.1.1.5:
access-list 100 deny ip 192.168.1.0 0.0.0.255 host 10.1.1.5 access-list 100 permit ip any any .
Where should the administrator place this ACL for the most efficient use of network resources?
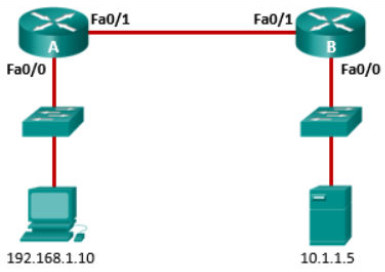
Explanation: The ACL should be placed inbound on the interface closest to the source (router A Fa0/0).
100. Which type of OSPFv2 packet is used to forward OSPF link change information?
Explanation: Link-state update packets carry OSPF link change information.
101. What protocol synchronizes with a private master clock or with a publicly available server on the internet?
Explanation: NTP (Network Time Protocol) synchronizes time with a master clock.
102. Which type of VPN allows multicast and broadcast traffic over a secure site-to-site VPN?
Explanation: GRE over IPsec supports multicast and broadcast traffic over a secure VPN.
103. An OSPF router has three directly connected networks; 10.0.0.0/16, 10.1.0.0/16, and 10.2.0.0/16. Which OSPF network command would advertise only the 10.1.0.0 network to neighbors?
Explanation: To advertise only the 10.1.0.0/16 network the wildcard mask used in the network command must match the first 16-bits exactly. To match bits exactly, a wildcard mask uses a binary zero. This means that the first 16-bits of the wildcard mask must be zero. The low order 16-bits can all be set to 1.
104. Refer to the exhibit. Which sequence of commands should be used to configure router A for OSPF?
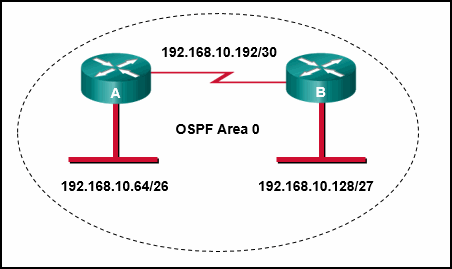
Explanation: OSPF network statements use wildcard masks and area numbers.
105. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 192.168.0.0 255.255.254.0. What wildcard mask would the administrator use in the OSPF network statement?
Explanation: The wildcard mask for 255.255.254.0 is 0.0.1.255.
106. How does virtualization help with disaster recovery within a data center?
Explanation: To advertise only the 10.1.0.0/16 network the wildcard mask used in the network command must match the first 16-bits exactly. To match bits exactly, a wildcard mask uses a binary zero. This means that the first 16-bits of the wildcard mask must be zero. The low order 16-bits can all be set to 1.
107. How does virtualization help with disaster recovery within a data center? (Case 2)
Explanation: Disaster recovery is how a company goes about accessing applications, data, and the hardware that might be affected during a disaster. Virtualization provides hardware independence which means the disaster recovery site does not have to have the exact equipment as the equipment in production. Server provisioning is relevant when a server is built for the first time. Although data centers do have backup generators, the entire data center is designed for disaster recovery. One particular data center could never guarantee that the data center itself would never be without power.
108. Refer to the exhibit. Which devices exist in the failure domain when switch S3 loses power?
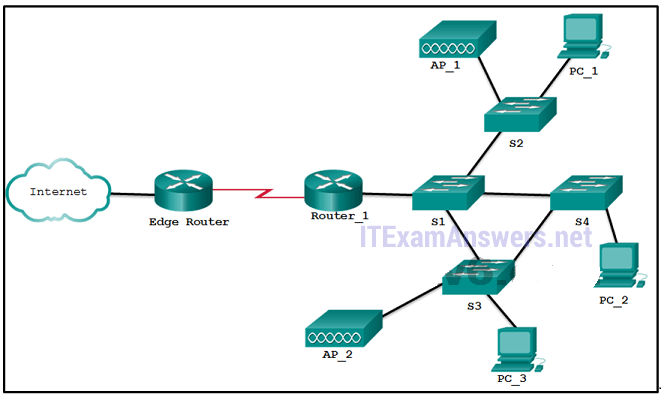
Explanation: The failure domain includes devices directly affected by S3's failure: PC_3 and AP_2.
109. Which set of access control entries would allow all users on the 192.168.10.0/24 network to access a web server that is located at 172.17.80.1, but would not allow them to use Telnet?
Explanation: The ACL permits HTTP to the web server and denies Telnet from the network.
110. Refer to the exhibit. A network administrator needs to add an ACE to the TRAFFIC-CONTROL ACL that will deny IP traffic from the subnet 172.23.16.0/20. Which ACE will meet this requirement?
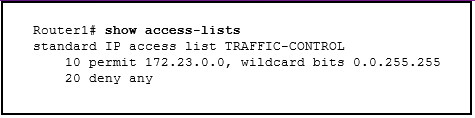
Explanation: The only filtering criteria specified for a standard access list is the source IPv4 address. The wild card mask is written to identify what parts of the address to match, with a 0 bit, and what parts of the address should be ignored, which a 1 bit. The router will parse the ACE entries from lowest sequence number to highest. If an ACE must be added to an existing access list, the sequence number should be specified so that the ACE is in the correct place during the ACL evaluation process.
111. Which step in the link-state routing process is described by a router building a link-state database based on received LSAs?
Explanation: Building the topology table involves creating the link-state database from LSAs.
112. What protocol uses agents, that reside on managed devices, to collect and store information about the device and its operation?
Explanation: SNMP uses agents on managed devices to collect and store information.
113. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 10.27.27.0 255.255.255.0. What wildcard mask would the administrator use in the OSPF network statement?
Explanation: The wildcard mask for 255.255.255.0 is 0.0.0.255.
114. When will an OSPF-enabled router transition from the Down state to the Init state?
Explanation: When OSPFv2 is enabled, the enabled Gigabit Ethernet 0/0 interface transitions from the Down state to the Init state. R1 starts sending Hello packets out all OSPF-enabled interfaces to discover OSPF neighbors to develop adjacencies with.
115. What type of traffic is described as having a high volume of data per packet?
Explanation: Video traffic has a high volume of data per packet.
116. What protocol is a vendor-neutral Layer 2 protocol that advertises the identity and capabilities of the host device to other connected network devices?
Explanation: LLDP is a vendor-neutral Layer 2 discovery protocol.
117. Which step in the link-state routing process is described by a router running an algorithm to determine the best path to each destination?
Explanation: The SPF algorithm calculates the best paths to all destinations.
118. Refer to the exhibit. Which conclusion can be drawn from this OSPF multiaccess network?
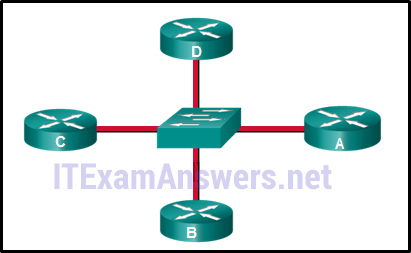
Explanation: On OSPF multiaccess networks, a DR is elected to be the collection and distribution point for LSAs sent and received. A BDR is also elected in case the DR fails. All other non-DR or BDR routers become DROTHER. Instead of flooding LSAs to all routers in the network, DROTHERs only send their LSAs to the DR and BDR using the multicast address 224.0.0.6. If there is no DR/BDR election, the number of required adjacencies is n(n-1)/2 = > 4(4-1)/2 = 6. With the election, this number is reduced to 3.
119. Refer to the exhibit. The network administrator has an IP address of 192.168.11.10 and needs access to manage R1. What is the best ACL type and placement to use in this situation?
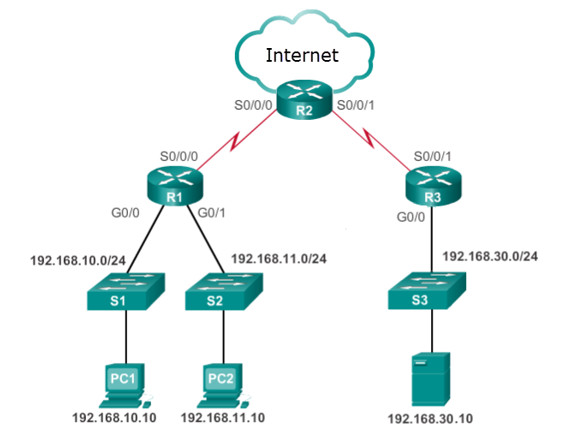
Explanation: Standard ACLs permit or deny packets based only on the source IPv4 address. Because all traffic types are permitted or denied, standard ACLs should be located as close to the destination as possible. Extended ACLs permit or deny packets based on the source IPv4 address and destination IPv4 address, protocol type, source and destination TCP or UDP ports and more. Because the filtering of extended ACLs is so specific, extended ACLs should be located as close as possible to the source of the traffic to be filtered. Undesirable traffic is denied close to the source network without crossing the network infrastructure.
120. Which type of VPN connects using the Transport Layer Security (TLS) feature?
Explanation: When a client negotiates an SSL VPN connection with the VPN gateway, it connects using Transport Layer Security (TLS). TLS is the newer version of SSL and is sometimes expressed as SSL/TLS. The two terms are often used interchangeably.
121. Which group of APIs are used by an SDN controller to communicate with various applications?
Explanation: Northbound APIs connect the SDN controller to applications.
122. A company has consolidated a number of servers and it is looking for a program or firmware to create and control virtual machines which have access to all the hardware of the consolidated servers. What service or technology would support this requirement?
Explanation: A Type-1 hypervisor runs directly on hardware and manages virtual machines.
123. What command would be used as part of configuring NAT or PAT to identify inside local addresses that are to be translated?
Explanation: An ACL identifies the inside local addresses that will be translated.
124. Anycompany has decided to reduce its environmental footprint by reducing energy costs, moving to a smaller facility, and promoting telecommuting. What service or technology would support this requirement?
Explanation: Cloud services reduce energy costs and support telecommuting.
125. Refer to the exhibit. An administrator is trying to back up the current running configuration of the router to a USB drive, and enters the command
copy usbflash0:/R1-config running-config
on the router command line. After removing the USB drive and connecting it to a PC, the administrator discovers that the running configuration was not properly backed up to the R1-config file. What is the problem?
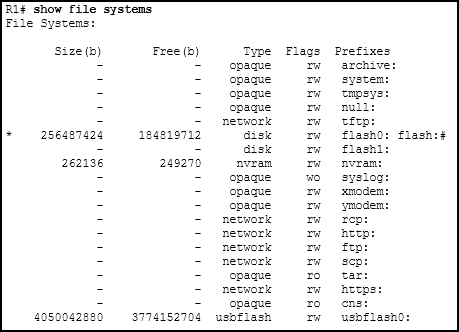
Explanation: The correct command is copy running-config usbflash0:/R1-config.
126. Which three types of VPNs are examples of enterprise-managed site-to-site VPNs? (Choose three.)
Explanation: IPsec VPN, DMVPN, and GRE over IPsec are enterprise-managed site-to-site VPNs.
127. Refer to the exhibit. Employees on 192.168.11.0/24 work on critically sensitive information and are not allowed access off their network. What is the best ACL type and placement to use in this situation?
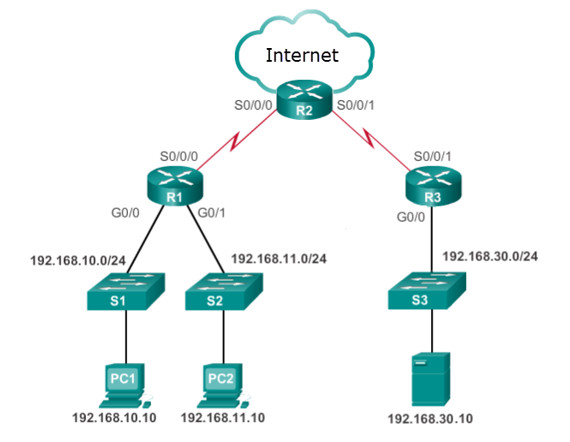
Explanation: A standard ACL inbound on the interface closest to the source restricts traffic from that network.
128. In an OSPF network which two statements describe the link-state database (LSDB)? (Choose two.)
Explanation: The LSDB is identical across all routers in an OSPF area and can be viewed with show ip ospf database.
129. In an OSPF network which OSPF structure is used to create the neighbor table on a router?
Explanation: The adjacency database contains the neighbor table.
130. What protocol is used in a system that consists of three elements--a manager, agents, and an information database?
Explanation: SNMP consists of a manager, agents, and a MIB (information database).
131. What type of traffic is described as not resilient to loss?
Explanation: Video traffic tends to be unpredictable, inconsistent, and bursty compared to voice traffic. Compared to voice, video is less resilient to loss and has a higher volume of data per packet.
132. Refer to the exhibit. Router R1 is configured with static NAT. Addressing on the router and the web server are correctly configured, but there is no connectivity between the web server and users on the Internet. What is a possible reason for this lack of connectivity?
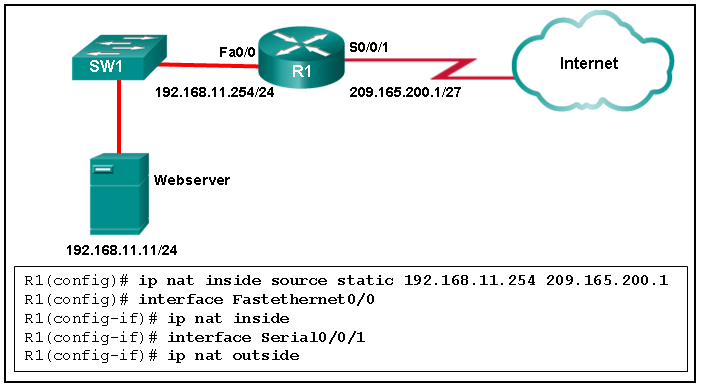
Explanation: The inside local address in the static NAT configuration may be incorrect.
133. Which type of API would be used to allow authorized salespeople of an organization access to internal sales data from their mobile devices?
Explanation: Private, or internal, APIs are used only within an organization and are for company access to data and services for internal use.
134. Refer to the exhibit. Which data format is used to represent the data for network automation applications?
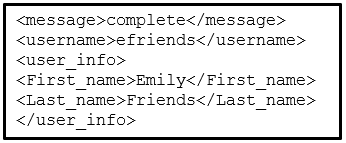
Explanation: Common data formats that are used in many applications including network automation and programmability include these:
JavaScript Object Notation (JSON) – In JSON, the data known as an object is one or more key/value pairs enclosed in braces { }. Keys must be strings within double quotation marks ” “. Keys and values are separated by a colon.
eXtensible Markup Language (XML) – In XML, the data is enclosed within a related set of tags data.
YAML Ain’t Markup Language (YAML) – In YAML, the data known as an object is one or more key value pairs. Key value pairs are separated by a colon without the use of quotation marks. YAML uses indentation to define its structure, without the use of brackets or commas.
135. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
access-list 101 permit udp 192.168.100.32 0.0.0.7 host 198.133.219.76 eq telnet .
If a packet with a source address of 198.133.219.100, a destination address of 198.133.219.170, and a protocol of 23 is received on the interface, is the packet permitted or denied?
Explanation: The source address (198.133.219.100) does not match the ACL's source range (192.168.100.32/29), so it is denied.
136. Refer to the exhibit. If no router ID was manually configured, what would router R1 use as its OSPF router ID?
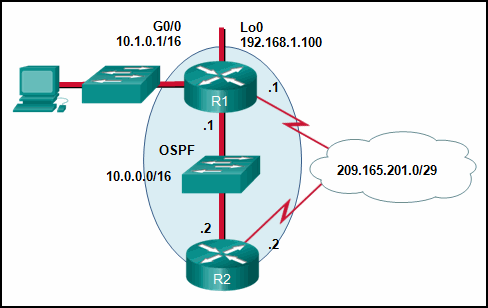
Explanation: OSPF uses the highest active IP address as the router ID if no router-id is configured.
137. What protocol is a vendor-neutral Layer 2 protocol that advertises the identity and capabilities of the host device to other connected network devices? (Duplicate)
Explanation: LLDP is a vendor-neutral Layer 2 discovery protocol.
138. Which type of VPN uses a hub-and-spoke configuration to establish a full mesh topology?
Explanation: DMVPN uses a hub-and-spoke configuration to establish a full mesh topology dynamically.
139. What is a characteristic of the REST API?
Explanation: REST accounts for more than 80% of all API types used for web services, making it the most widely used web service API.
141. A student, doing a summer semester of study overseas, has taken hundreds of pictures on a smartphone and wants to back them up in case of loss. What service or technology would support this requirement?
Explanation: Cloud services provide backup and storage accessible from anywhere.
142. Consider the following access list that allows IP phone configuration file transfers from a particular host to a TFTP server. Which method would allow the network administrator to modify the ACL and include FTP transfers from any source IP address?
R1(config)# access-list 105 permit udp host 10.0.70.23 host 10.0.54.5 range 1024 5000
R1(config)# access-list 105 deny ip any any
R1(config)# interface gi0/0
R1(config-if)# ip access-group 105 out
Explanation: To modify an existing ACL, it must be removed and recreated with the new entries.
143. Which three statements are generally considered to be best practices in the placement of ACLs? (Choose three.)
Explanation: Extended ACLs should be placed as close as possible to the source IP address, so that traffic that needs to be filtered does not cross the network and use network resources. Because standard ACLs do not specify a destination address, they should be placed as close to the destination as possible. Placing a standard ACL close to the source may have the effect of filtering all traffic, and limiting services to other hosts. Filtering unwanted traffic before it enters low-bandwidth links preserves bandwidth and supports network functionality. Decisions on placing ACLs inbound or outbound are dependent on the requirements to be met.
144. Match the term to the web link component. (Not all options are used.)
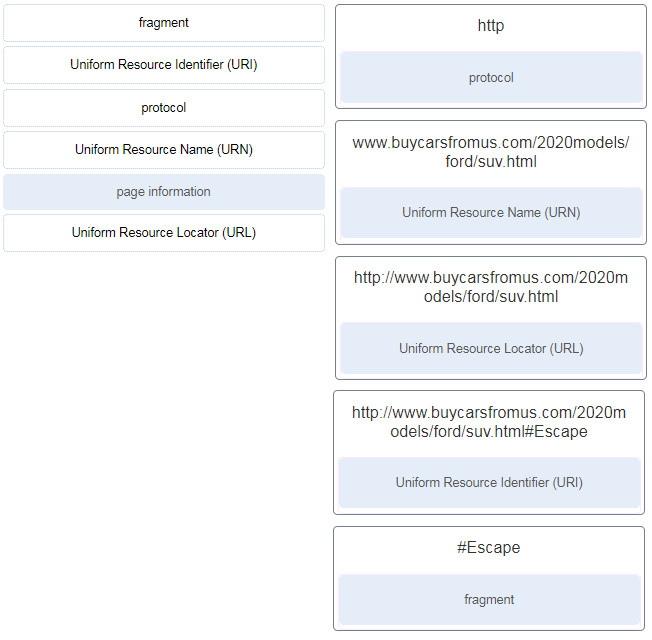
Explanation: URL components: protocol, URN, URL, URI, and fragment.
| Component | Example |
|---|---|
| protocol | http |
| URN | www.buycarsfromus.com/2020models/ford/suv.html |
| URL | http://www.buycarsfromus.com/2020models/ford/suv.html |
| URI | http://www.buycarsfromus.com/2020models/ford/suv.html#Escape |
| fragment | #Escape |
145. What command would be used as part of configuring NAT or PAT to display all static translations that have been configured?
Explanation: show ip nat translations displays all NAT translations, including static ones.
146. A network administrator modified an OSPF-enabled router to have a hello timer setting of 20 seconds. What is the new dead interval time setting by default?
Explanation: The dead interval is 4 times the hello interval by default: 20 × 4 = 80 seconds.
147. Which type of VPN is the preferred choice for support and ease of deployment for remote access?
Explanation: SSL VPNs are preferred for remote access due to ease of deployment and support.
148. What type of traffic is described as predictable and smooth?
Explanation: Voice traffic is predictable and smooth compared to data and video.
149. Which queuing mechanism has no provision for prioritizing or buffering but simply forwards packets in the order they arrive?
Explanation: FIFO (First In, First Out) forwards packets in the order they arrive.
150. Refer to the exhibit. A network administrator has configured OSPFv2 on the two Cisco routers. The routers are unable to form a neighbor adjacency. What should be done to fix the problem on router R2?
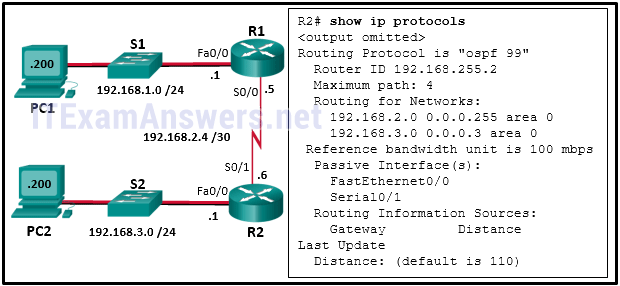
Explanation: The interface is configured as passive, preventing OSPF adjacency. Remove passive-interface.
151. A network administrator is troubleshooting an OSPF problem that involves neighbor adjacency. What should the administrator do?
Explanation: Hello and dead intervals must match for OSPF neighbors to form adjacency.
152. Refer to the exhibit. Internet privileges for an employee have been revoked because of abuse but the employee still needs access to company resources. What is the best ACL type and placement to use in this situation?
Explanation: – Standard ACLs permit or deny packets based only on the source IPv4 address. Because all traffic types are permitted or denied, standard ACLs should be located as close to the destination as possible. – Extended ACLs permit or deny packets based on the source IPv4 address and destination IPv4 address, protocol type, source and destination TCP or UDP ports and more. Because the filtering of extended ACLs is so specific, extended ACLs should be located as close as possible to the source of the traffic to be filtered. Undesirable traffic is denied close to the source network without crossing the network infrastructure.
153. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
access-list 100 permit tcp 192.168.10.0 0.0.0.255 172.17.200.0 0.0.0.255 eq www .
If a packet with a source address of 192.168.10.244, a destination address of 172.17.200.56, and a protocol of 80 is received on the interface, is the packet permitted or denied?
Explanation: The packet matches the ACL's source, destination, and protocol (HTTP port 80), so it is permitted.
154. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use applications such as Nmap, SuperScan, and Angry IP Scanner?
Explanation: Nmap and similar tools are used for port scanning and network discovery.
155. What command would be used as part of configuring NAT or PAT to display any dynamic PAT translations that have been created by traffic?
Explanation: show ip nat translations displays both static and dynamic NAT/PAT entries.
156. An administrator is configuring single-area OSPF on a router. One of the networks that must be advertised is 172.16.91.0 255.255.255.192. What wildcard mask would the administrator use in the OSPF network statement?
Explanation: The wildcard mask for 255.255.255.192 is 0.0.0.63.
157. What type of traffic is described as requiring latency to be no more than 400 milliseconds (ms)?
Explanation: Video traffic requires latency of no more than 400 ms.
158. Refer to the exhibit. Which two configurations would be used to create and apply a standard access list on R1, so that only the 10.0.70.0/25 network devices are allowed to access the internal database server? (Choose two.)
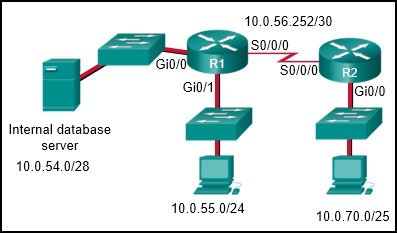
Explanation: A standard ACL permits the 10.0.70.0/25 network and is applied outbound on the interface.
159. A network administrator is writing a standard ACL that will deny any traffic from the 172.16.0.0/16 network, but permit all other traffic. Which two commands should be used? (Choose two.)
Explanation: To deny traffic from the 172.16.0.0/16 network, the access-list 95 deny 172.16.0.0 0.0.255.255 command is used. To permit all other traffic, the access-list 95 permit any statement is added.
160. Refer to the exhibit. The company has decided that no traffic initiating from any other existing or future network can be transmitted to the Research and Development network. Furthermore, no traffic that originates from the Research and Development network can be transmitted to any other existing or future networks in the company. The network administrator has decided that extended ACLs are better suited for these requirements. Based on the information given, what will the network administrator do?
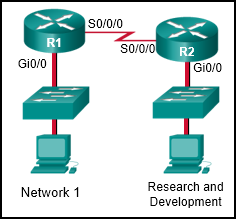
Explanation: Extended ACLs in both directions on the R&D interface will enforce the traffic restrictions.
161. What protocol uses smaller stratum numbers to indicate that the server is closer to the authorized time source than larger stratum numbers?
Explanation: In NTP, lower stratum numbers indicate closer proximity to the authoritative time source.
162. Refer to the exhibit. If no router ID was manually configured, what would router Branch1 use as its OSPF router ID?
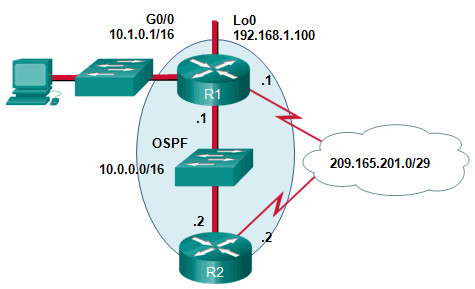
Explanation: In OSPFv2, a Cisco router uses a three-tier method to derive its router ID. The first choice is the manually configured router ID with the router-id command. If the router ID is not manually configured, the router will choose the highest IPv4 address of the configured loopback interfaces. Finally if no loopback interfaces are configured, the router chooses the highest active IPv4 address of its physical interfaces.
163. Match the HTTP method with the RESTful operation. (Duplicate)
| HTTP Method | RESTful Operation |
|---|---|
| POST | create |
| GET | read |
| PUT/PATCH | update |
| DELETE | delete |
164. Refer to the exhibit. A web designer calls to report that the web server web-s1.cisco.com is not reachable through a web browser. The technician uses command line utilities to verify the problem and to begin the troubleshooting process. Which two things can be determined about the problem? (Choose two.)
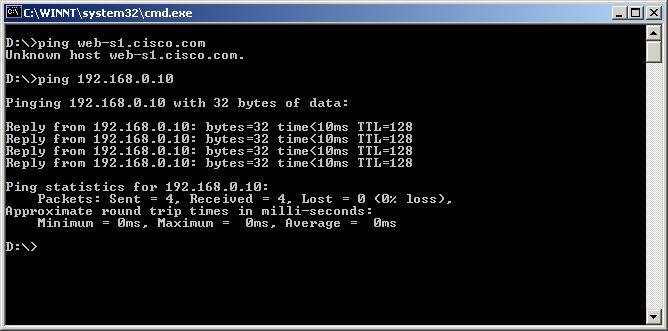
Explanation: The successful result of the ping to the IP address indicates that the network is operational and the web server is online. However, the fact that the ping to the domain name of the server fails indicates there is a DNS issue, namely that the host cannot resolve the domain name to its associated IP address.
165. What type of traffic is described as tending to be unpredictable, inconsistent, and bursty?
Explanation: Video traffic is unpredictable, inconsistent, and bursty.
166. Match the functions to the corresponding layers. (Not all options are used.)
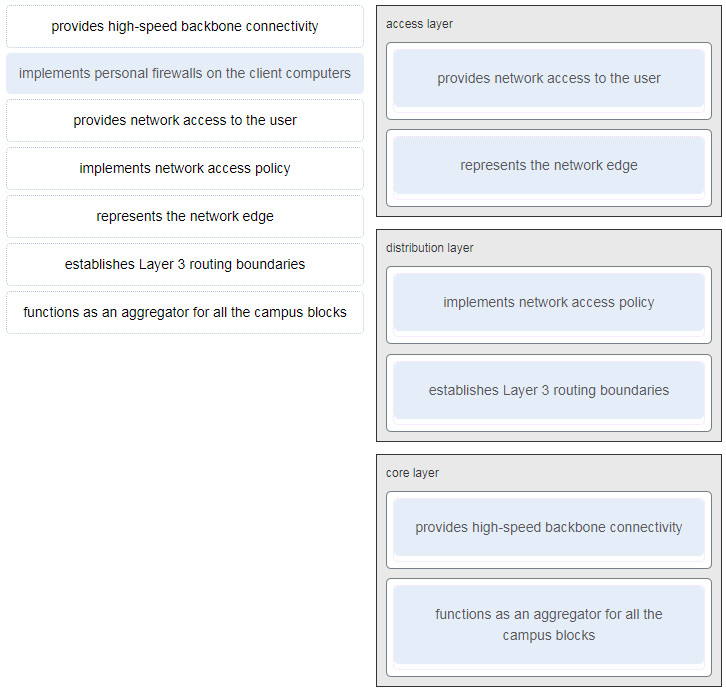
| Access Layer | Distribution Layer | Core Layer |
|---|---|---|
| provides network access to the user | implements network access policy | provides high-speed backbone connectivity |
| represents the network edge | establishes Layer 3 routing boundaries | functions as an aggregator for all the campus blocks |
167. What type of traffic is described as consisting of traffic that requires a higher priority if interactive?
Explanation: Interactive data traffic requires higher priority.
168. Which type of VPN provides a flexible option to connect a central site with branch sites?
Explanation: DMVPN provides a flexible hub-and-spoke VPN solution.
169. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use fuzzers?
Explanation: Fuzzers are used to discover security vulnerabilities by sending malformed input.
170. Refer to the exhibit. A network administrator has configured a standard ACL to permit only the two LAN networks attached to R1 to access the network that connects to R2 G0/1 interface, but not the G0/0 interface. When following the best practices, in what location should the standard ACL be applied?
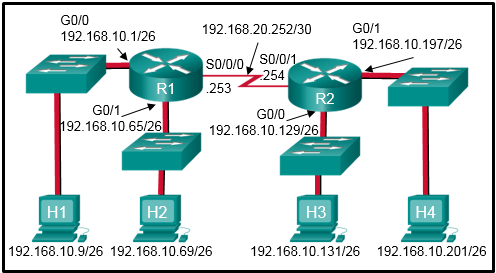
Explanation: Standard ACLs should be placed close to the destination, so outbound on R2 G0/0.
171. Two OSPF-enabled routers are connected over a point-to-point link. During the ExStart state, which router will be chosen as the first one to send DBD packets?
Explanation: In the ExStart state, the two routers decide which router will send the DBD packets first. The router with the higher router ID will be the first router to send DBD packets during the Exchange state
172. Which step in the link-state routing process is described by a router sending Hello packets out all of the OSPF-enabled interfaces?
Explanation: OSPF-enabled routers must recognize each other on the network before they can share information. An OSPF-enabled router sends Hello packets out all OSPF-enabled interfaces to determine if neighbors are present on those links. If a neighbor is present, the OSPF-enabled router attempts to establish a neighbor adjacency with that neighbor.
173. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use forensic tools?
Explanation: Forensic tools are used to detect evidence of hacking or malware.
174. Refer to the exhibit. A network administrator has configured OSPFv2 on the two Cisco routers but PC1 is unable to connect to PC2. What is the most likely problem?
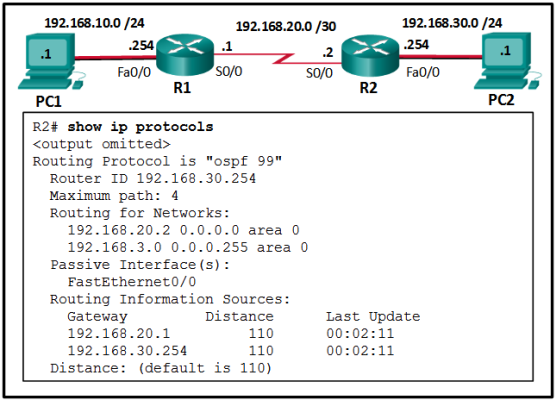
Explanation: If a LAN network is not advertised using OSPFv2, a remote network will not be reachable. The output displays a successful neighbor adjacency between router R1 and R2 on the interface S0/0 of both routers.
175. ABCTech is investigating the use of automation for some of its products. In order to control and test these products, the programmers require Windows, Linux, and MAC OS on their computers. What service or technology would support this requirement?
Explanation: Virtualization allows multiple operating systems to run on a single machine.
176. A network engineer has noted that some expected network route entries are not displayed in the routing table. Which two commands will provide additional information about the state of router adjacencies, timer intervals, and the area ID? (Choose two.)
Explanation: The show ip ospf interface command will display routing table information that is already known. The show running-configuration and show ip protocols commands will display aspects of the OSPF configuration on the router but will not display adjacency state details or timer interval details.
177. Which type of VPN involves the forwarding of traffic over the backbone through the use of labels distributed among core routers?
Explanation: MPLS VPN uses labels to forward traffic across the provider backbone.
178. Which type of VPN involves a nonsecure tunneling protocol being encapsulated by IPsec?
Explanation: GRE (nonsecure) is encapsulated by IPsec to provide security.
179. A company has contracted with a network security firm to help identify the vulnerabilities of the corporate network. The firm sends a team to perform penetration tests to the company network. Why would the team use hacking operation systems?
Explanation: Hacking operating systems come preloaded with penetration testing tools.
180. What command would be used as part of configuring NAT or PAT to identify an interface as part of the external global network?
Explanation: The ip nat outside command identifies the external (global) interface.
181. To avoid purchasing new hardware, a company wants to take advantage of idle system resources and consolidate the number of servers while allowing for multiple operating systems on a single hardware platform. What service or technology would support this requirement?
Explanation: Server virtualization takes advantage of idle resources and consolidates the number of required servers. This also allows for multiple operating systems to exist on a single hardware platform.
182. Which type of VPN routes packets through virtual tunnel interfaces for encryption and forwarding?
Explanation: IPsec VTI uses virtual tunnel interfaces for encryption and forwarding.
183. Which step in the link-state routing process is described by a router flooding link-state and cost information about each directly connected link?
Explanation: Link-state advertisements are flooded to exchange link-state information.
184. What type of traffic is described as using either TCP or UDP depending on the need for error recovery?
Explanation: Data traffic can use TCP or UDP based on error recovery requirements.
185. Refer to the exhibit. The company CEO demands that one ACL be created to permit email traffic to the internet and deny FTP access. What is the best ACL type and placement to use in this situation?
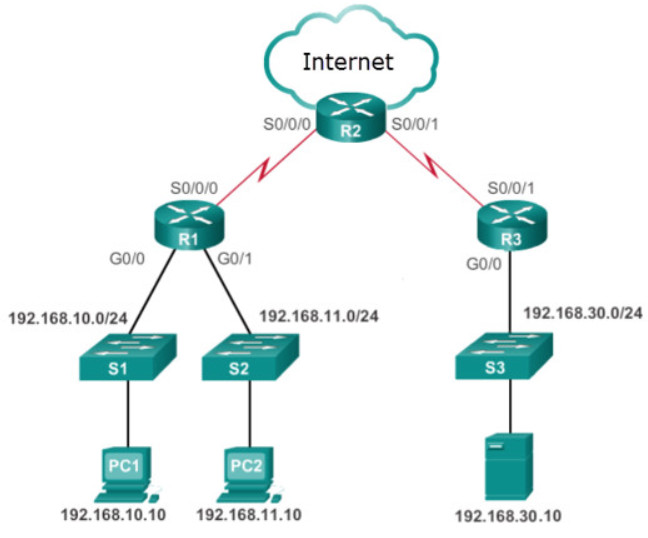
Explanation: An extended ACL on the outbound WAN interface can permit email and deny FTP.
186. What command would be used as part of configuring NAT or PAT to define a pool of addresses for translation?
Explanation: The ip nat pool command defines a pool of addresses for NAT.
187. What is the name of the layer in the Cisco borderless switched network design that is considered to be the backbone used for high-speed connectivity and fault isolation?
Explanation: The three layers of the Cisco borderless switch network design are access, distribution, and core. The access layer switches are the ones used to connect end devices to the network. The distribution layer switches accept connections from access layer switches and provides switching, routing, and access policy functions. The core layer is called the backbone and core switches commonly have high-speed redundant connections.
188. An ACL is applied inbound on router interface. The ACL consists of a single entry:
access-list 210 permit tcp 172.18.20.0 0.0.0.47 any eq ftp
If a packet with a source address of 172.18.20.40, a destination address of 10.33.19.2, and a protocol of 21 is received on the interface, is the packet permitted or denied?
Explanation: The source address 172.18.20.40 is within the range 172.18.20.0/27 (wildcard 0.0.0.47), and protocol is FTP (port 21), so it is permitted.
189. What type of traffic is described as consisting of traffic that gets a lower priority if it is not mission-critical?
Explanation: Non-mission-critical data traffic gets lower priority.
190. Which OSPF table is identical on all converged routers within the same OSPF area?
Explanation: The topology table (link-state database) is identical across all routers in an OSPF area.
191. An ACL is applied inbound on a router interface. The ACL consists of a single entry: access-list 100 permit tcp 192.168.10.0 0.0.0.255 any eq www . If a packet with a source address of 192.168.10.45, a destination address of 10.10.3.27, and a protocol of 80 is received on the interface, is the packet permitted or denied?
Explanation: The packet matches the source network and HTTP (port 80), so it is permitted.
192. What protocol allows the manager to poll agents to access information from the agent MIB?
Explanation: SNMP allows managers to poll agents and access MIB information.
193. Match each component of a WAN connection to its description. (Not all options are used.)
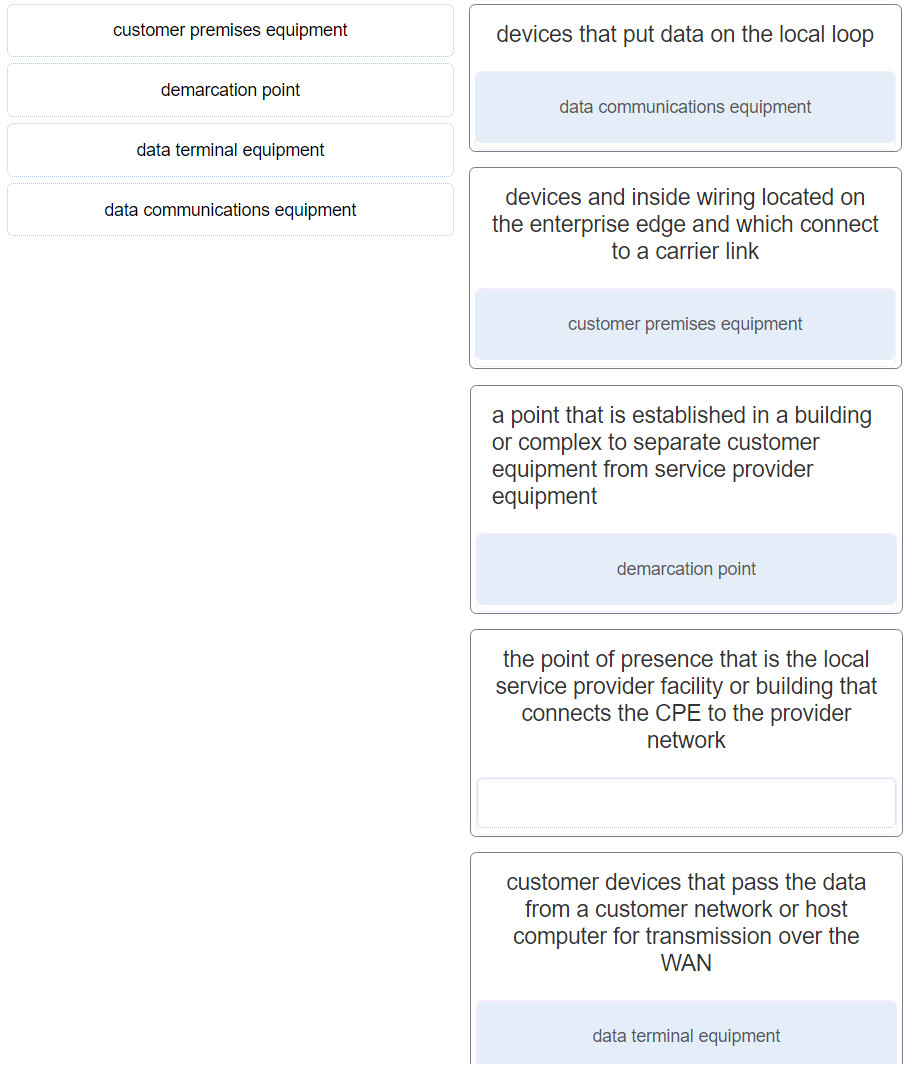
Explanation: Match WAN components to their descriptions.
194. What type of traffic is described as being able to tolerate a certain amount of latency, jitter, and loss without any noticeable effects?
Explanation: Voice traffic can tolerate some latency, jitter, and loss.
195. What term describes adding a value to the packet header, as close to the source as possible, so that the packet matches a defined policy?
Explanation: Traffic marking adds a value to the packet header to match a policy.
196. Which three traffic-related factors would influence selecting a particular WAN link type? (Choose three.)
Explanation: The traffic-related factors that influence selecting a particular WAN link type include the type of traffic, amount of traffic, quality requirements, and security requirements. Quality requirements include ensuring that traffic that cannot tolerate delay gets priority treatment as well as important business transactional traffic.
197. What command would be used as part of configuring NAT or PAT to link the inside local addresses to the pool of addresses available for PAT translation?
Explanation: The ip nat inside source list 14 pool POOL-STAT overload command links inside addresses to a PAT pool.
198. What protocol is a vendor-neutral Layer 2 discovery protocol that must be configured separately to transmit and receive information packets?
Explanation: LLDP must be configured separately to transmit and receive information.
199. An ACL is applied inbound on a router interface. The ACL consists of a single entry:
access-list 210 permit tcp 172.18.20.0 0.0.0.31 172.18.20.32 0.0.0.31 eq ftp .
If a packet with a source address of 172.18.20.55, a destination address of 172.18.20.3, and a protocol of 21 is received on the interface, is the packet permitted or denied?
Explanation: The source address 172.18.20.55 is not in the range 172.18.20.0/27, so it is denied.
200. Refer to the exhibit. Corporate policy demands that access to the server network be restricted to internal employees only. What is the best ACL type and placement to use in this situation?
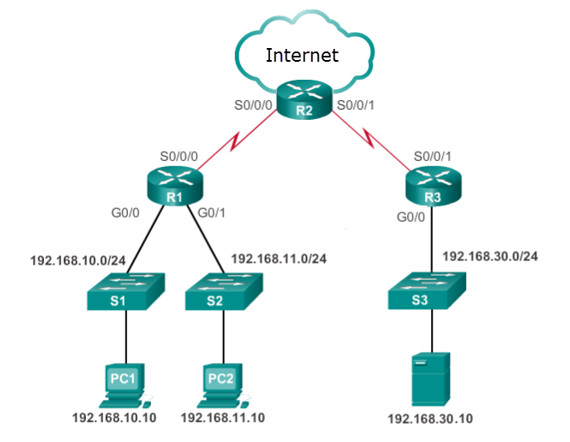
Explanation: An extended ACL outbound on the interface connected to the server network restricts access to internal employees.
201. A technician is working on a Layer 2 switch and notices that a %CDP-4-DUPLEX_MISMATCH message keeps appearing for port G0/5. What command should the technician issue on the switch to start the troubleshooting process?
Explanation: show interface g0/5 displays the duplex settings and helps diagnose the mismatch.
202. Which virtual resource would be installed on a network server to provide direct access to hardware resources?
Explanation: Type 1 hypervisors, the hypervisor is installed directly on the server or networking hardware. Then, instances of an OS are installed on the hypervisor, as shown in the figure. Type 1 hypervisors have direct access to the hardware resources. Therefore, they are more efficient than hosted architectures. Type 1 hypervisors improve scalability, performance, and robustness.
203. Refer to the exhibit. A network administrator has configured a standard ACL to permit only the two LAN networks attached to R1 to access the network that connects to R2 G0/1 interface. When following the best practices, in what location should the standard ACL be applied?
Explanation: Standard ACLs should be placed close to the destination, so outbound on R2 G0/1.
204. Which OSPF database is identical on all converged routers within the same OSPF area?
Explanation: Regardless of which OSPF area a router resides in, the adjacency database, routing table, and forwarding database are unique for each router. The link-state database lists information about all other routers within an area and is identical across all OSPF routers participating in that area.
205. What are two features to consider when creating a named ACL? (Choose two.)
Explanation: The following summarizes the rules to follow for named ACLs:
Assign a name to identify the purpose of the ACL.
Names can contain alphanumeric characters.
Names cannot contain spaces or punctuation.
It is suggested that the name be written in CAPITAL LETTERS.
Entries can be added or deleted within the ACL.
206. Match the RESTful API method to CRUD function.
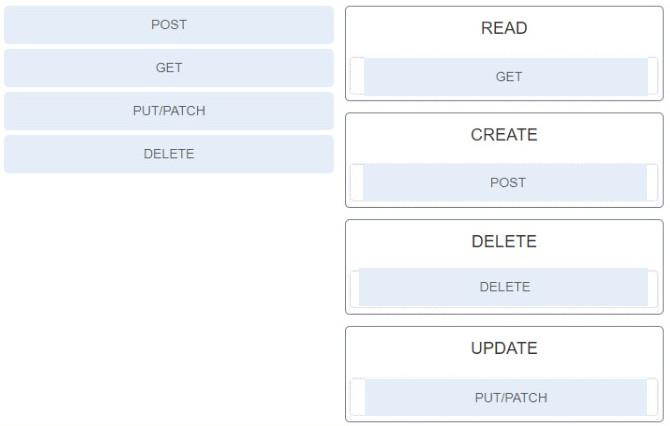
Explanation: Match RESTful methods to CRUD operations.
207. What type of traffic is described as requiring at least 384 Kbps of bandwidth?
Explanation: Video traffic requires at least 384 Kbps of bandwidth.
208. Which step in the link-state routing process is described by a router inserting best paths into the routing table?
Explanation: Choosing the best route inserts the best paths into the routing table.
209. Anycompany has decided to reduce its environmental footprint by reducing energy costs, moving to a smaller facility, and promoting telecommuting. What service or technology would support this requirement? (Duplicate)
Explanation: Cloud services support telecommuting and reduce energy costs.
210. Which QoS technique smooths packet output rate?
Explanation: Traffic shaping smooths the packet output rate by buffering excess packets.
211. Refer to the exhibit. The company has provided IP phones to employees on the 192.168.10.0/24 network and the voice traffic will need priority over data traffic. What is the best ACL type and placement to use in this situation?
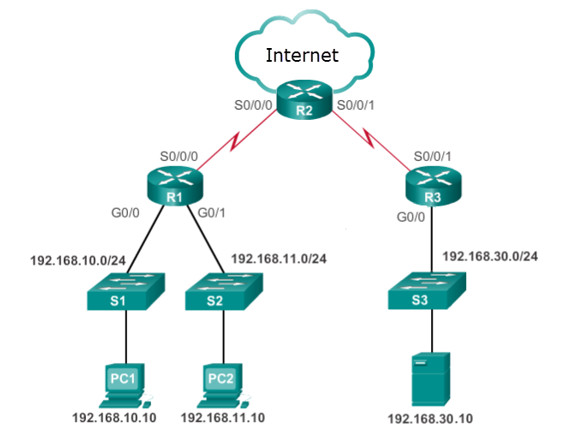
Explanation: Standard ACLs permit or deny packets based only on the source IPv4 address. Because all traffic types are permitted or denied, standard ACLs should be located as close to the destination as possible. Extended ACLs permit or deny packets based on the source IPv4 address and destination IPv4 address, protocol type, source and destination TCP or UDP ports and more. Because the filtering of extended ACLs is so specific, extended ACLs should be located as close as possible to the source of the traffic to be filtered. Undesirable traffic is denied close to the source network without crossing the network infrastructure.
212. A network technician is configuring SNMPv3 and has set a security level of SNMPv3 authPriv. What is a feature of using this level?
Explanation: SNMPv3 authPriv level provides authentication (HMAC-MD5 or HMAC-SHA) and privacy (encryption).
🚀 Ace Your CCNA Exam - Complete Study Pack!
Get 500+ exam-realistic questions, Packet Tracer labs, and detailed explanations.
Understanding the CCNA 3 v7.0 Final Exam (ENSA)
Passing the CCNA 3 v7.0 Final Exam for Enterprise Networking, Security, and Automation (ENSA) requires a comprehensive understanding of advanced networking concepts, including OSPF, network security, WAN technologies, QoS, and network automation. This final exam tests your ability to configure, verify, and troubleshoot complex enterprise networks.
Why the ENSA Final Exam Matters for Your Networking Career
The CCNA 3 v7.0 Final Exam is the culmination of the Enterprise Networking, Security, and Automation course. It validates your knowledge of OSPF routing, access control lists (ACLs), Network Address Translation (NAT), VPNs, IPsec, Quality of Service (QoS), and network automation. Passing this exam demonstrates your readiness to design, implement, and manage enterprise-grade networks—skills that are highly valued by employers in the networking industry.
Key Topics Covered in the Final Exam
Our verified answers address common exam questions on:
- OSPF Routing: Single-area and multi-area OSPF, DR/BDR election, OSPF states, and route summarization.
- Network Security: ACLs (standard and extended), firewall technologies, and security best practices.
- WAN Technologies: Private and public WAN connections, Ethernet WAN, MPLS, and VPNs.
- Network Address Translation (NAT): Static NAT, dynamic NAT, PAT, and NAT troubleshooting.
- VPNs and IPsec: Site-to-site VPNs, remote access VPNs, GRE, DMVPN, and IPsec protocols.
- Quality of Service (QoS): Traffic classification, marking, policing, shaping, and queuing.
- Network Automation: REST APIs, JSON, XML, YAML, and SDN concepts.
- Virtualization: Type 1 and Type 2 hypervisors, and cloud computing.
Many questions present a network topology and ask you to identify the correct configuration, troubleshoot issues, or select the best solution. Understanding the interplay between different technologies is critical for success.
Common Pitfalls to Avoid
Students often confuse standard and extended ACLs – standard ACLs filter only on source IP, while extended ACLs can filter on source/destination IP, protocol, and port. Another common mistake is mixing up NAT address types – inside local vs. inside global, outside local vs. outside global. Also, remember that OSPF DR/BDR election is based on priority (highest wins) and then router ID.
When practicing with our answers, avoid memorizing letter choices (A, B, C, D). Cisco often reorders options. Focus on the concept behind each correct answer. For example, instead of remembering "option B is the correct NAT type", learn the difference between static NAT, dynamic NAT, and PAT.
Study Strategies That Work
To retain this material long-term, combine our exam answers with hands-on practice. Use Packet Tracer to configure OSPF, ACLs, NAT, and VPNs. Set up a site-to-site VPN between two routers. Implement QoS policies and verify traffic prioritization. This practical approach cements the theory from the ENSA curriculum.
We also recommend creating flashcards for key terms: OSPF, DR, BDR, ACL, NAT, PAT, VPN, IPsec, GRE, DMVPN, QoS, CoS, DSCP, JSON, XML, YAML, SDN, hypervisor, and cloud computing. Quiz yourself daily until you can define each term without hesitation.
How to Use This Answer Page Effectively
Our goal at CoursMooc.com is to provide accurate, up-to-date answers for the latest CCNA v7 curriculum. For each question, we include an explanation—not just the correct choice. Read those explanations carefully. If you find a concept unclear, refer to the official Cisco NetAcad course materials or our additional tutorials linked below.
We regularly update this page to match any changes in the exam. If you notice discrepancies, please let us know through the comments. Your feedback helps other learners succeed.
What's Next After the ENSA Final Exam?
After completing the CCNA 3 v7.0 Final Exam, you have completed the full CCNA v7 curriculum (CCNA 1, 2, and 3). The next step is to prepare for the official CCNA 200-301 certification exam, which covers a broad range of networking topics. You can also explore more advanced certifications like CCNP or specialized tracks in security, wireless, or data center.
Final Tips for Exam Day
Before starting the real exam:
- Get a good night's sleep – fatigue leads to misreading questions.
- Read each question twice. Some ask "Which two statements are correct?" – don't just pick one answer.
- Manage your time. You typically have 50-60 minutes for 40-50 questions. Skip difficult ones and return later.
- Look for keywords like "not", "except", or "only". One word changes the entire meaning.
- Trust your first instinct unless you find clear evidence you misread.
Remember: The CCNA v7 curriculum emphasizes practical troubleshooting. If you can explain why a NAT translation fails or why an OSPF neighbor won't form, you're ready. Use our answers to verify your thinking, then reinforce with simulation tools. Good luck on your exam – and on your journey to networking expertise.